
AI Agent Authentication: How Do You Secure AI Agents Acting for Humans?

Artificial intelligence is moving beyond answering questions. AI agents can now schedule meetings, access databases, execute workflows, manage cloud resources, and interact with business applications without requiring human intervention at every step.
But this growing autonomy introduces a critical security question.
How do you authenticate a machine that is acting on behalf of a human?
Traditional authentication systems were designed to verify human users or software applications. AI agents introduce another layer of complexity because they can independently decide which tools to use and what actions to perform.
An AI agent might need access to customer records, financial information, internal applications, or cloud infrastructure. Without proper identity management, organizations risk giving automated systems more authority than intended.
This is where AI Agent Authentication becomes essential.
Understanding how AI agents establish identity, receive permissions, and securely interact with enterprise systems is becoming a fundamental requirement for building trustworthy AI applications.
What Is AI Agent Authentication?
AI Agent Authentication is the process of verifying the identity of an artificial intelligence agent before allowing it to interact with applications, APIs, databases, or other digital resources.
In simple terms, authentication answers one question:
Is this AI agent really the system it claims to be?
Consider a human employee accessing a company application.
The employee typically authenticates using a password, passkey, security key, or another approved authentication method.
Once authenticated, the system determines which resources the employee can access.
AI agents require a similar process, but their identities and permissions must account for automated execution.
An AI agent may operate continuously, communicate with multiple systems, and perform actions without direct human supervision.
For example, imagine a financial assistant powered by AI.
The assistant receives a request:
"Prepare a summary of our outstanding invoices and identify overdue payments."
To complete the task, the AI agent may need to:
- Connect to the company's accounting software.
- Retrieve invoice information.
- Analyze payment records.
- Generate a financial summary.
- Send the report to an authorized employee.
Each interaction involves sensitive business information.
The organization must verify that the agent is legitimate and ensure it accesses only the information required for the task.
Authentication establishes the agent's identity. Authorization determines what that identity is permitted to do.
Both are necessary for secure AI automation.
Why Traditional Authentication Is Not Enough
Traditional identity and access management systems generally focus on two categories.
Human identities: Employees, customers, administrators, and other individuals accessing applications.
Machine identities: Servers, applications, services, and automated processes communicating with other systems.
AI agents belong to the broader machine identity category, but they introduce additional challenges.
Unlike conventional applications that follow predefined instructions, AI agents can dynamically select tools and plan sequences of actions.
An agent may begin with a simple information request and later determine that it needs access to additional systems.
This creates questions that traditional authentication alone cannot answer.
Who authorized the agent to perform the task?
Which human or organization is responsible for its actions?
How long should the agent retain access?
What happens when the agent attempts an unexpected operation?
Organizations need identity systems that connect machine authentication with human authorization, task-specific permissions, and continuous monitoring.
Why AI Agent Identity Matters
As organizations deploy more autonomous systems, managing their identities becomes increasingly important.
A poorly secured AI agent can expose sensitive data or execute unauthorized operations.
An agent with excessive permissions might accidentally modify records, delete resources, or trigger workflows outside its intended responsibilities.
Strong AI agent identity management helps organizations establish accountability.
Every agent should have an identifiable owner, defined permissions, and a record of its activities.
The goal is not simply to allow AI agents to connect.
The goal is to ensure that every connection and action is authorized, traceable, and appropriate.
Why AI Agent Authentication Is Becoming Critical
AI agents are increasingly being integrated into business operations.
Organizations are experimenting with autonomous assistants for customer support, software development, infrastructure management, financial analysis, and operational automation.
These systems often interact with several applications during a single workflow.
A customer support agent, for example, might access a CRM platform, retrieve order information, update a support ticket, and initiate a refund request.
Each action introduces a security decision.
The Problem of Excessive Permissions
One of the most significant risks is granting AI agents more access than necessary.
Suppose an organization gives an AI assistant full administrative access to its customer database.
The assistant only needs to retrieve customer details.
However, its credentials also allow it to modify or delete records.
If the agent makes an incorrect decision or processes malicious instructions, the consequences could extend far beyond the original task.
This is why the principle of least privilege is essential.
An AI agent should receive only the permissions required to complete its assigned work.
The Challenge of Delegated Authority
AI agents frequently act on behalf of human users.
This introduces a distinction between the identity of the agent and the authority of the person requesting the action.
Consider an employee asking an AI assistant to retrieve a confidential document.
The system must verify several things.
First, is the AI agent authentic?
Second, is the employee authorized to access the document?
Third, has the employee or an approved organizational policy authorized the agent to retrieve it?
Finally, is the requested action within the agent's permitted scope?
A secure system should evaluate these conditions before granting access.
Simply authenticating the agent does not prove that every action it performs is authorized.
The Risk of Prompt Injection
AI agents frequently process information from external sources, including websites, emails, documents, and APIs.
Some of this information may contain malicious instructions designed to influence the agent.
This attack technique is commonly known as prompt injection.
For example, an AI agent summarizing an email might encounter embedded instructions telling it to send confidential information to an external address.
The agent must treat the email as untrusted content rather than as an authoritative instruction.
Authentication alone cannot prevent prompt injection.
Organizations also need authorization checks, tool restrictions, data validation, and security controls that operate independently of the language model.
Why Identity Must Be Established Before Autonomy
The more independently an AI agent operates, the more important its identity becomes.
Organizations should know which agent initiated an action, whose authority it used, what permissions were granted, and which resources were affected.
Without this information, investigating security incidents becomes difficult.
A reliable identity architecture provides the foundation for secure autonomous operations.
Building AI agents that can perform tasks is only one part of the challenge. Ensuring they perform those tasks under the correct identity and authority is equally important.
How AI Agent Authentication Works
AI Agent Authentication typically involves several components working together.
These components establish the agent's identity, connect it to an authorized user or workload, and control access to enterprise resources.
Step 1: Establish a Unique Agent Identity
Every production AI agent should have a distinct identity.
This identity may be represented by a service principal, workload identity, or another identity record managed by an organization's identity provider.
For example, an organization might register separate identities for:
- Customer support agents.
- Financial reporting agents.
- Infrastructure monitoring agents.
- Software development agents.
Each identity should have an identifiable owner and defined responsibilities.
Using separate identities helps organizations distinguish one agent's actions from another's.
It also makes access reviews, credential rotation, and incident investigations easier.
Step 2: Authenticate the Agent
Before accessing protected resources, the agent must prove its identity.
Depending on the architecture, this may involve:
OAuth 2.0 client authentication: The agent authenticates as a registered client when requesting access tokens.
Mutual TLS: Both communicating systems authenticate using certificates.
Workload identity: The execution environment provides a verifiable identity that the receiving system trusts.
Signed assertions: The agent or its hosting workload presents a cryptographically signed statement proving its identity.
Authentication methods should match the environment in which the agent operates.
For example, a cloud-hosted agent may use a managed workload identity rather than storing long-lived credentials.
This reduces the risk associated with exposed API keys.
Step 3: Establish Human Delegation
When an agent acts on behalf of a person, the system must establish the person's authority separately from the agent's identity.
OAuth 2.0 authorization flows can support this model.
A user may authorize an application to access specific resources without sharing their password.
The authorization server can issue a token representing the approved access.
In some architectures, token exchange allows a trusted service to obtain a new token for a downstream service while preserving relevant delegation context.
However, the exact behavior depends on the identity provider, token claims, and resource server configuration.
A token should never be treated as proof of unlimited authority.
The receiving system must validate the token and enforce its intended scope.
Step 4: Issue Limited Access Tokens
After successful authentication and authorization, the agent may receive an access token.
The token represents specific access rights.
For example, an agent preparing a sales report may receive permission to read selected sales records.
It should not automatically receive permission to delete customer accounts or modify financial transactions.
Secure token design should consider:
- Intended audience.
- Allowed operations.
- Token expiration.
- Resource restrictions.
- Delegated user context.
- Revocation and session termination mechanisms.
Short-lived tokens can reduce the period during which stolen credentials remain useful.
However, token expiration alone does not guarantee immediate revocation.
Systems handling sensitive operations may require additional authorization checks.
Step 5: Enforce Authorization at the Resource
The receiving application or API must evaluate whether the requested action is permitted.
This is a critical distinction.
An authenticated agent is not necessarily an authorized agent.
For example, an AI assistant may successfully authenticate to a document management platform.
That does not mean it should access every document in the organization.
The platform must enforce document-level permissions and relevant business policies.
For delegated operations, authorization may need to consider both the agent's permissions and the user's permissions.
Step 6: Record Agent Activity
Every significant action should generate an audit record.
Useful audit information includes:
- Agent identity.
- Initiating user or approved automation context.
- Requested operation.
- Target resource.
- Authorization decision.
- Timestamp.
- Execution outcome.
Sensitive credentials and unnecessary personal information should not be stored in logs.
These records help organizations investigate incidents, monitor unusual behavior, and demonstrate operational accountability.
A Simple Architecture for Secure AI Agents
Consider an employee asking an AI assistant to update a customer record.
The process might work as follows:
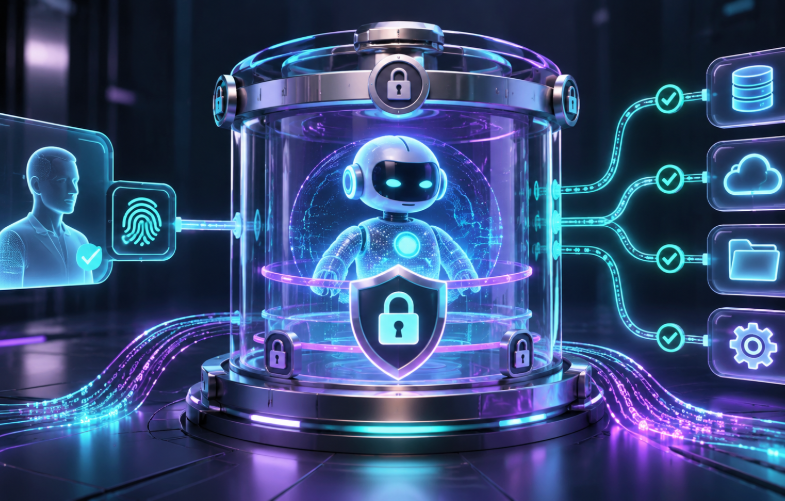
Human User → AI Application → Agent Identity → Authorization Service → Enterprise API → Audit System
The user authenticates to the application.
The application establishes the user's request and the agent's identity.
An authorization service determines whether the requested operation is allowed.
The agent calls the enterprise API using an appropriately scoped credential.
The API validates the credential and independently enforces access rules.
Finally, the system records the action.
This separation prevents the AI model from becoming the sole authority over sensitive operations.
Technologies Used for AI Agent Authentication
Several established identity and security technologies can support AI agent authentication.
The appropriate combination depends on the organization's infrastructure, security requirements, and level of agent autonomy.
OAuth 2.0
OAuth 2.0 is an authorization framework that enables applications to obtain limited access to protected resources.
It is particularly useful when AI agents interact with third-party applications or act under delegated user authority.
For example, an AI scheduling assistant may use OAuth 2.0 to access a user's calendar.
The assistant receives a token with approved permissions instead of requiring the user's account password.
Advantages:
- Supports delegated access.
- Enables limited permission scopes.
- Works with many enterprise APIs.
- Supports established token management patterns.
Limitations:
OAuth 2.0 does not independently solve every AI agent identity problem.
Organizations must still determine which agent is acting, whose authority applies, and how individual actions are approved.
OpenID Connect
OpenID Connect, commonly called OIDC, adds an identity layer to OAuth 2.0.
It allows applications to verify information about an authenticated user.
OIDC is useful when AI applications need to establish the identity of the human initiating a workflow.
However, an ID token intended for user authentication should not be substituted for an API access token.
Workload Identity
Workload identity allows software running in a trusted environment to authenticate without relying on manually managed, long-lived secrets.
Cloud platforms commonly provide mechanisms for assigning identities to applications and services.
For AI agents running in managed cloud environments, workload identity can simplify authentication and reduce credential exposure.
The main consideration is ensuring that the workload identity is correctly bound to the intended runtime.
Mutual TLS
Mutual Transport Layer Security, or mTLS, allows two communicating systems to authenticate each other using certificates.
It can be useful for service-to-service communication in controlled enterprise environments.
For example, an internal AI agent may communicate with a sensitive financial API through an mTLS-protected connection.
However, certificate-based authentication does not replace application-level authorization.
SPIFFE and SPIRE
SPIFFE provides a framework for assigning identities to software workloads.
SPIRE is an implementation that can issue and manage workload identities.
These technologies can be useful in distributed environments where AI agents run across containers, clusters, or infrastructure platforms.
They help establish workload identity without depending entirely on static credentials.
API Gateways and Policy Engines
API gateways provide a controlled entry point for requests to enterprise services.
They can validate tokens, apply rate limits, and enforce selected access policies.
Policy engines can evaluate more detailed authorization rules.
For example, a policy might allow an agent to retrieve invoices but require additional approval before changing payment details.
A gateway is not a replacement for resource-level authorization, but it can provide a consistent security enforcement layer.
Choosing the Right Technology
For a small AI application, an existing identity provider and properly scoped OAuth tokens may be sufficient.
For enterprise environments with multiple autonomous agents, a more comprehensive architecture may be necessary.
This could include workload identities, centralized policy enforcement, credential management, audit logging, and human approval workflows.
The goal should be to reuse proven identity technologies rather than inventing a completely separate authentication system for AI.
Best Practices for Secure AI Agent Authentication
Secure AI agent systems require more than choosing an authentication protocol.
Organizations must design identity, authorization, and operational controls around how agents actually behave.
Assign a Unique Identity to Every Agent
Avoid using one shared credential for multiple agents.
Shared identities make it difficult to determine which agent performed a particular action.
Individual identities support accountability and more precise access control.
Apply Least-Privilege Access
Agents should receive only the permissions required for their responsibilities.
A reporting agent may need read-only access.
An operational agent may require limited write permissions.
Administrative access should be reserved for explicitly approved scenarios.
Use Short-Lived Credentials
Avoid embedding permanent API keys or passwords in prompts, source code, or configuration files.
Where possible, use managed identities and short-lived access tokens.
Store necessary secrets in a dedicated secrets management system.
Separate Authentication From Authorization
Authentication verifies identity.
Authorization determines whether a particular action is permitted.
Both decisions must be enforced by trusted infrastructure rather than relying solely on the AI model's instructions.
Require Approval for High-Risk Actions
Not every agent operation should execute automatically.
Sensitive actions may include:
- Transferring money.
- Deleting production data.
- Changing security configurations.
- Publishing confidential information.
- Modifying access permissions.
For these operations, organizations should consider explicit human approval or another independently enforced authorization mechanism.
Implement Zero Trust Principles
Zero trust security assumes that no user, device, or workload should receive unrestricted access simply because it operates inside a trusted network.
For AI agents, this means verifying identity and authorization for each protected interaction.
An agent that successfully accessed one system should not automatically gain access to another.
Monitor Agent Behavior
Authentication logs alone may not reveal harmful activity.
Organizations should also monitor tool usage, resource access, unusual request patterns, and sensitive operations.
For example, an agent that normally retrieves ten records but suddenly requests thousands may require additional investigation.
Monitoring should support both security detection and operational troubleshooting.
Treat External Content as Untrusted
AI agents may process documents, emails, websites, and other external material.
These sources should not be allowed to redefine security policies or grant permissions.
Tool permissions and authorization decisions must remain outside the control of untrusted content.
Review Agent Permissions Regularly
AI agent permissions should evolve as business requirements change.
Organizations should periodically review:
- Active agent identities.
- Assigned permissions.
- Credential expiration.
- Agent ownership.
- Unused identities.
- Access to sensitive resources.
Agents that are no longer required should be disabled, and their credentials should be revoked.
Performance, Cost, and Security Considerations
AI agent authentication introduces additional security checks into automated workflows.
These checks can affect system performance, infrastructure complexity, and operating costs.
However, the objective should not be to eliminate authentication overhead.
It should be to implement security controls efficiently.
Authentication Latency
Every authentication or authorization request introduces some processing time.
For example, an agent may need to obtain an access token before calling a protected API.
If the agent performs hundreds of operations, repeatedly requesting new tokens can create unnecessary overhead.
Organizations can reduce this overhead through appropriate token reuse, secure caching, and efficient authorization architecture.
However, caching must respect token expiration, revocation requirements, and permission changes.
High-risk actions may require fresh authorization decisions even when a valid token already exists.
Infrastructure Costs
AI agent identity management may require additional infrastructure.
Potential components include:
- Identity providers.
- Token services.
- API gateways.
- Secrets management systems.
- Policy engines.
- Monitoring platforms.
- Audit storage.
Costs depend on the number of agents, authentication volume, vendor pricing, deployment architecture, and compliance requirements.
Organizations should evaluate the complete operating cost rather than focusing only on initial implementation.
Credential Management
Credential management becomes more challenging as the number of AI agents grows.
A small organization may initially operate five agents.
A larger enterprise may eventually manage hundreds or thousands of agent instances.
Without automation, tracking credentials and permissions can become difficult.
Automated identity provisioning, credential rotation, and lifecycle management can reduce operational effort.
Security Versus Convenience
Developers may be tempted to simplify authentication by giving agents broad permissions.
This approach can accelerate early experimentation.
However, it also increases the potential impact of compromised credentials or unintended agent behavior.
Production systems should prioritize controlled access over unrestricted convenience.
Scalability
Authentication infrastructure must support the expected volume of agent interactions.
An AI workflow may call several APIs to complete a single user request.
As concurrent agent activity increases, token validation and authorization services may become important performance considerations.
Organizations should test authentication infrastructure under realistic workloads.
Useful measurements include authentication latency, authorization decision time, failed requests, token issuance volume, and service availability.
There is no universal performance benchmark that applies to every AI agent architecture.
The appropriate targets depend on the application and its security requirements.
Real-World Use Cases of AI Agent Authentication
AI agent authentication is relevant wherever autonomous systems interact with protected resources.
Enterprise Customer Support
Consider an organization deploying an AI-powered customer support assistant.
The assistant can retrieve order details, check shipment status, and update support tickets.
Without proper identity controls, the assistant could potentially access customer records outside the intended support context.
A secure architecture assigns the assistant a dedicated identity.
The application establishes the authenticated customer or support employee's context.
The backend then verifies whether the requested information can be accessed.
For example, the assistant may retrieve a customer's order status but cannot access unrelated customer accounts.
Refunds or account modifications may require additional authorization.
Business benefit: Organizations can automate routine support activities while maintaining access restrictions and accountability.
AI Agents in Cloud Operations
Cloud infrastructure teams increasingly use automation to monitor applications, investigate incidents, and recommend operational changes.
An AI operations agent might identify a service failure and suggest restarting an application.
However, restarting a service is different from deleting a production database.
These actions should not share the same authorization requirements.
A secure cloud operations agent may receive read-only monitoring access by default.
Limited operational permissions can be granted for specific approved workflows.
High-impact changes may require human confirmation.
Business benefit: Teams can accelerate incident investigation without granting unrestricted infrastructure access.
Financial Reporting Automation
A financial reporting agent may collect information from accounting platforms, databases, and business applications.
The agent could prepare cash flow summaries, identify overdue invoices, and generate management reports.
These tasks often require access to sensitive financial data.
A secure implementation uses a dedicated agent identity with carefully restricted permissions.
The agent may retrieve approved financial records but cannot modify payment instructions or initiate transfers.
Every access request can be logged for review.
Business benefit: Finance teams can automate reporting while separating analytical access from transaction authority.
Healthcare Administration
Healthcare organizations may use AI agents for appointment scheduling, administrative documentation, and operational coordination.
These workflows can involve sensitive patient information.
An agent should access only the information necessary for its assigned task.
For example, an appointment scheduling agent may need access to provider availability and selected patient scheduling details.
It should not automatically receive access to complete medical histories.
Organizations must also consider applicable privacy and security regulations.
Business benefit: Administrative workflows can become more efficient without treating automation as an exemption from access-control requirements.
IoT and Connected Device Management
AI agents can also support Internet of Things environments.
Consider a connected-device platform managing sensors across multiple facilities.
An AI operations agent might detect unusual device behavior, investigate connectivity issues, and recommend corrective actions.
It may need to interact with device management APIs, cloud services, and operational dashboards.
Authentication ensures that the agent is a recognized workload.
Authorization determines which devices and operations it can access.
For example, the agent may be permitted to restart a specific device but not change firmware across an entire fleet.
This distinction becomes especially important when AI agents interact with physical systems.
Business benefit: Organizations can automate device operations while maintaining control over potentially disruptive actions.
AI Agent Authentication vs Traditional Authentication
AI agent authentication builds on established identity technologies, but the operational requirements differ from conventional user authentication.
Human Authentication
Human authentication establishes the identity of an individual.
Common methods include passwords, passkeys, security keys, and multifactor authentication.
A human user generally initiates an interactive session.
The system then applies permissions associated with that user's identity.
Traditional Machine Authentication
Machine authentication establishes the identity of software applications, services, or devices.
Common mechanisms include certificates, workload identities, service accounts, and cryptographic credentials.
These identities often support predefined service-to-service operations.
AI Agent Authentication
AI agent authentication establishes the identity of an agent or its trusted execution environment.
However, secure AI agent systems also need to manage the authority under which the agent acts.
This becomes important because agents can dynamically select actions and tools.
For example, a conventional application may execute a predefined API request.
An AI agent may decide which API to call based on a user's request and information retrieved from other systems.
The authentication mechanism may be similar, but the authorization context is more complex.
Authentication vs Authorization vs Delegation
These concepts are closely related but serve different purposes.
Authentication: Verifies the identity of the agent or user.
Authorization: Determines which resources and operations are permitted.
Delegation: Establishes the authority granted to an agent or application to act on behalf of another party.
Consider a user asking an AI assistant to send an email.
Authentication verifies the assistant's identity.
Delegation establishes that the assistant has permission to act for the user.
Authorization determines whether it may access the mailbox and send the requested message.
A secure system needs all three.
API Keys vs OAuth Tokens
API keys are often used to authenticate applications.
They can be straightforward to implement, especially for server-to-server integrations.
However, static API keys may be difficult to manage securely when they are long-lived or shared across multiple agents.
OAuth-based architectures can provide more flexible mechanisms for delegated access and scoped permissions.
Still, OAuth is not automatically secure.
Token validation, scope enforcement, credential storage, and authorization policies must be implemented correctly.
The choice depends on the application architecture and security requirements.
Why Authentication Alone Cannot Make AI Agents Safe
An authenticated AI agent can still make mistakes.
It may misunderstand a request, select the wrong tool, or process malicious external instructions.
Authentication proves identity, not correctness.
Organizations must combine identity controls with application security, tool restrictions, validation, monitoring, and appropriate human oversight.
This layered approach is essential for production-grade AI systems.
How to Implement AI Agent Authentication
Organizations planning to deploy autonomous AI systems should begin with a clear identity and authorization architecture.
Step 1: Identify Every AI Agent
Create an inventory of agents that interact with protected systems.
Record each agent's purpose, owner, execution environment, and required integrations.
This establishes visibility into the organization's non-human identities.
Step 2: Define Required Permissions
Determine which resources each agent needs.
Separate read operations from write operations.
Identify actions that require additional approval.
Avoid granting broad permissions simply to simplify development.
Step 3: Select an Authentication Mechanism
Choose authentication methods based on the agent's environment.
Cloud-hosted agents may use managed workload identities.
Agents accessing third-party APIs may use OAuth 2.0.
Internal service communication may use certificates or other cryptographic workload credentials.
Step 4: Establish Delegated Authority
For agents acting on behalf of users, define how user authorization is obtained and represented.
Ensure the agent cannot exceed the permissions granted by the user and applicable organizational policies.
Use supported authorization flows rather than sharing user passwords.
Step 5: Enforce Authorization Independently
Protected APIs should validate credentials and enforce permissions.
Do not rely on prompts such as "only access authorized data" as the primary security control.
Security policies must be enforced by trusted software components.
Step 6: Add Monitoring and Audit Logging
Record important agent actions and authorization decisions.
Monitor unusual behavior and failed access attempts.
Protect audit records against unauthorized modification.
Step 7: Test Failure Scenarios
Before production deployment, test what happens when:
- An agent presents an expired token.
- A credential is revoked.
- An agent requests an unauthorized operation.
- A user loses access to a resource.
- An external document contains malicious instructions.
- An agent attempts to access another tenant's data.
These tests help validate whether security controls operate correctly under unexpected conditions.
Step 8: Review and Improve
Identity management is an ongoing process.
As agents gain new capabilities, their permissions and security controls should be reviewed.
Organizations should regularly evaluate whether existing authorization policies still match business requirements.
FAQs
What is AI Agent Authentication?
AI Agent Authentication verifies the identity of an artificial intelligence agent before it accesses protected applications, APIs, or resources.
It helps organizations distinguish legitimate agents from unauthorized workloads and supports secure access management.
How do AI agents authenticate themselves?
AI agents can authenticate using OAuth client authentication, workload identities, certificates, signed assertions, or other supported machine authentication mechanisms.
The appropriate method depends on the agent's execution environment and the systems it needs to access.
How do you authenticate an AI agent acting on behalf of a human?
The system authenticates the agent and separately establishes the human user's identity and delegated authority.
An authorization service then determines whether the agent may perform the requested operation.
OAuth-based delegation and token exchange can support this architecture when correctly implemented.
What is the difference between AI agent authentication and authorization?
Authentication verifies who or what is making a request.
Authorization determines whether the authenticated identity can perform a particular action.
Both are required to protect enterprise systems.
Can AI agents use OAuth 2.0?
Yes.
AI agents can use OAuth 2.0 to obtain limited access to protected APIs and applications.
OAuth is especially useful for delegated access, but implementations must correctly validate tokens and enforce permissions.
What is non-human identity management?
Non-human identity management refers to managing identities assigned to software, services, workloads, devices, and automated systems.
AI agents are an increasingly important category of non-human identity because they can initiate actions across multiple systems.
What are the biggest security risks associated with AI agents?
Important risks include excessive permissions, credential theft, prompt injection, unauthorized data access, insecure tool execution, and insufficient audit visibility.
These risks require multiple layers of security controls.
Does zero trust security apply to AI agents?
Yes.
Zero trust principles require systems to verify identity and enforce authorization rather than automatically trusting agents based on their network location or previous access.
This is particularly important for autonomous systems operating across enterprise applications.
Do AI agents need separate identities?
Production AI agents should generally have distinct, manageable identities.
Separate identities improve accountability, access control, credential management, and incident investigation.
The exact identity model may depend on whether the organization manages individual agents, agent instances, or shared execution workloads.
Can AI agent authentication prevent prompt injection?
Not by itself.
Authentication verifies identity, while prompt injection attempts to manipulate an agent's behavior through untrusted content.
Organizations should combine authentication with authorization enforcement, tool restrictions, input handling, monitoring, and approval mechanisms.
An AI agent should never have more authority than the human it represents. True AI security begins with verified identity, controlled access, and accountability

Conclusion
AI agents are changing how software interacts with enterprise systems. As they gain the ability to retrieve information, execute workflows, and make operational decisions, organizations must establish reliable ways to verify their identities and control their permissions.
AI Agent Authentication provides an essential foundation, but it must work alongside delegated authorization, least-privilege access, monitoring, and secure application design.
The organizations that build these controls into their AI architecture from the beginning will be better positioned to scale automation without sacrificing accountability.
Build Secure AI Agent Systems With Infolitz
Developing AI agents is only part of building a reliable automation platform. The underlying identity, API, cloud, and security architecture must also support controlled access and dependable operations.
At Infolitz Software Pvt. Ltd., we help businesses design and develop AI-powered applications, cloud integrations, and secure software systems.
Planning an AI agent application or reviewing the security of your existing AI workflows? Contact Infolitz to discuss your requirements and explore a practical implementation approach.


